Unified Security Platform | Always-On AI Analyst Layer

Clarity
Not Chaos.

Catch the One That Matters.

CiBRAI brings signals from endpoints, cloud, identity, and network into one operational view. Powered by sovereign agentic AI, it works with your existing tools and adds an always-on AI analyst layer that groups events, adds context, and prioritises what matters.

Works with existing tools
Less noise, more signal
Clear audit trail
Unified Incident View
Single priority incident in focus
Correlated activity14 events
Priority incident
Credential misuse followed by lateral movement across cloud and identity.
Cloud · Identity · Endpoint
Suppressed noise
Repetitive endpoint telemetry grouped and deprioritised.
Endpoint
Watching
Network beacon pattern kept in observation queue.
Network

What happened

Initial access
Identity anomaly detected.
Context added
Asset and user role matched.
Next action
Contain, revoke token.
AI analyst summary
This is the one to act on first.

Agentic AI grouped related signals, removed noise, and prioritised a real incident with business context so your SOC can contain it fast.

Guided playbooks

Revoke compromised identity sessionRun
Isolate affected endpointRun
Notify incident ownerRun

Executive-ready reporting

For security teams
Less manual triage. Clearer investigations. Faster response.
For boards and executives
Plain-English incident summaries and a defensible audit trail.
Board-ready summary generated
Signal in
Endpoint, cloud, identity, and network visibility in one place.
Context added
Agentic AI groups events, enriches them, and surfaces what matters.
Action guided
Playbooks and automation help contain incidents quickly.
Reporting clear
Leadership, compliance, and audit teams get a clean trail.
Why change now

The traditional SOC is yesterday's paradigm.

Security teams are not short on telemetry. They are short on clarity. More dashboards do not create better decisions. CiBRAI replaces fragmented workflows with a unified platform and an always-on AI analyst layer.

Too many alerts

Analysts waste time triaging fragments instead of seeing the full incident story.

Too little context

Critical signals are buried across disconnected tools, duplicate events, and manual handoffs.

Too much manual effort

Response, escalation, and reporting still depend on people stitching evidence together under pressure.

Before vs after
Clarity-led operating model

Legacy SOC

×Fragmented alerts spread across multiple consoles.
×Investigation quality depends on who can manually correlate fastest.
×Reporting is reconstructed after the event for leaders and auditors.

CiBRAI model

One operational view across endpoint, cloud, identity, and network.
Agentic AI groups events, adds context, and prioritises action.
Guided playbooks and clear audit trails support response and reporting.
Product story
See the full attack story, not a pile of alerts.
Always-on AI analyst
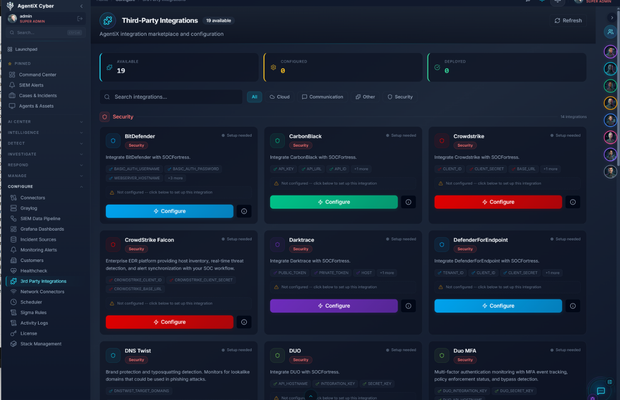
CiBRAI third-party integrations — connect your existing tools
🔗
Third-Party Integrations Connect endpoints, cloud, identity, and network tools — no rip-and-replace
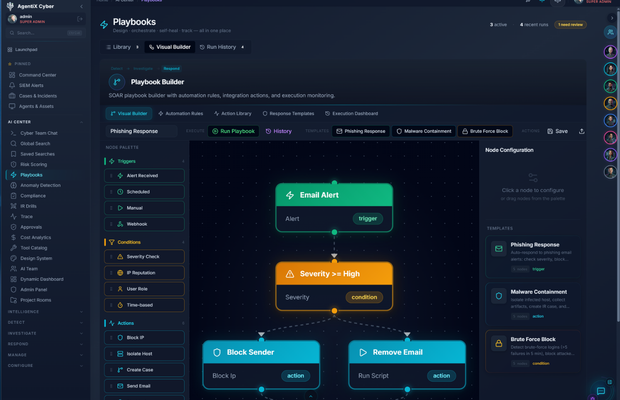
CiBRAI guided playbooks — structured response from detection to containment
📋
Guided Playbooks Structured response steps from detection through to containment — every time
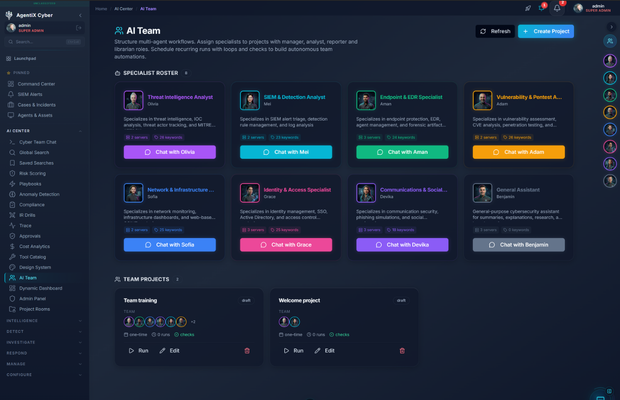
CiBRAI AI tools — always-on analyst layer for triage and response
🤖
AI Analyst Tools Always-on AI that groups events, adds context, and prioritises what matters
Why CiBRAI

Readable for executives. Useful for security teams.

CiBRAI unifies signals across your environment — then gives every audience the view they need. Analysts get prioritised incidents and guided response. Leaders get clear summaries they can act on.

01
Unified signal view Connect your existing tools — endpoints, cloud, identity, and network — into one operational picture without replacing what already works.
02
Guided playbook response Structured response steps guide your team from detection through to containment — consistently, across every shift and every analyst.
03
Always-on AI analyst layer AI groups events, adds context, and surfaces the one incident that matters — working alongside your team 24/7 without fatigue.
Built for your audiences

One message, tuned for every decision-maker.

The same platform speaks to technical buyers, operations teams, and senior stakeholders — without becoming abstract or overly technical.

CIOs & CTOs

Reduce tool sprawl and operational drag.

Consolidate visibility and make security operations easier to govern across the organisation.

CISOs

See real priorities faster.

Improve SOC efficiency, gain clearer oversight, and focus teams on the incidents that matter.

Security Teams

Less triage. Better investigations.

Spend less time on duplicate alerts and more time on guided containment and validation.

Boards & Leaders

Understand risk without translation.

Get plain-English summaries, defensible reporting, and a clearer view of business impact.

SOC augmentation

Augment your SOC without adding more chaos.

CiBRAI does not replace your team. It helps your team move faster, focus better, and respond with more confidence — with a unified platform designed for the way modern security operations actually work.

Always-on AI analyst working alongside your team 24/7.
One clear incident view — not a pile of disconnected alerts.
Guided response and reporting built into every investigation.
⚡ CiBRAI platform — live view
CiBRAI unified security platform screenshot — SOC augmentation in action
Always-on · Always clear
Research Reports — CiBRAI
CiBRAI Research

CiBRAI Research Reports

Practitioner-led research from CiBRAI and Gadget Access on the questions boards, CISOs, SOC leaders and Defence suppliers are being asked right now: when AI can be trusted to act, how the global threat picture has changed, and what Defence security membership actually requires.

All reports are free. Select one, some or all of them, enter your work email and we’ll send the download links straight to your inbox.

The library

Tick the reports you want. Your selection carries through to the request form below.

0 selected
Flagship
CiBRAI Research 2026
AI Trust
Under Attack
CiBRAI Research Report · 2026

AI Trust Under Attack

What evidence, authority and recovery conditions should exist before an AI system is permitted to influence or execute a cyber defence action?

A 40-page, practitioner-led report for boards, CISOs, SOC leaders, security architects and platform builders. Trust is not permission granted once; it is permission continuously earned.

  • The CiBRAI AI Trust Fabric — eight interdependent dimensions, Trust Contracts and evidence chains.
  • Bounded autonomy — a six-level Autonomy Ladder, human oversight gates and adversarial controls.
  • Assurance that operates — lifecycle gates, a five-level maturity model and a 90-day implementation path.
  • Executive action — board questions, decisions to make now and the Trust Manifesto.
40 pagesAugust 2026Boards & CISOsSOC leaders
New
CiBRAI Global Intelligence
Global Threat
Report 2026
CiBRAI × Gadget Access · 2026

Global Threat Report 2026

The new control plane is trust. Cybersecurity, agentic AI, quantum resilience, scams, fraud and threat actors, with evidence to 31 August 2026.

A 98-page intelligence report for boards, CISOs, security leaders, risk owners and policy teams on how the threat picture has shifted and what it means for control design.

  • Cybersecurity — attack speed has compressed to seconds; defenders must run a fast compromise clock and year-long persistence detection at the same time.
  • Agentic AI — delegating authority without cryptographically binding intent, identity and action creates scope drift and unsanctioned effects.
  • Quantum resilience — migration urgency comes from data lifetime plus replacement lead time, not from guesses about when quantum computers arrive.
  • Scams and fraud — fraud now runs as a programmable supply chain; transaction-level controls remain the decisive defence.
98 pagesSeptember 2026Boards & risk ownersPolicy teams
New
Gadget Access Business Guide
DISP
Explained
Gadget Access Business Guide · 2026

DISP Explained for Australian Defence Suppliers

What Defence Industry Security Program membership requires and how to prepare your business. Build Defence readiness into the business plan.

A 14-page plain-English guide for Australian suppliers who want to win and keep Defence work, from the team behind CiBRAI’s advisory practice.

  • When membership is mandatory — PROTECTED information, weapons and ordnance, or an explicit contract security condition.
  • The four security domains — governance, personnel, physical and information/cyber security, scoped to the work you do.
  • Essential Eight at Maturity Level 2 — what all eight strategies mean in practice across the systems that matter.
  • Continuous assurance — annual security reports, 14-day change reporting and the evidence you need to keep.
14 pagesSeptember 2026Defence suppliersOwners & GMs
Free download

Request your reports

Enter your work email and we’ll send the download links for the reports you’ve chosen. Nothing else unless you ask.

Which reports would you like?
Choose one, some or all.

We’ll email you the download links and occasional CiBRAI Research updates. No spam, unsubscribe any time. See our Privacy Policy.

No sales follow-up unless you ask
Links delivered by email
Unsubscribe any time
Put the research to work

Every report ends with decisions to make now. If one of them raises a question about your own environment, we offer a complimentary 30-minute call. No pitch, no follow-up unless you ask.


Want the next report as soon as it’s published?